Malware Research Team

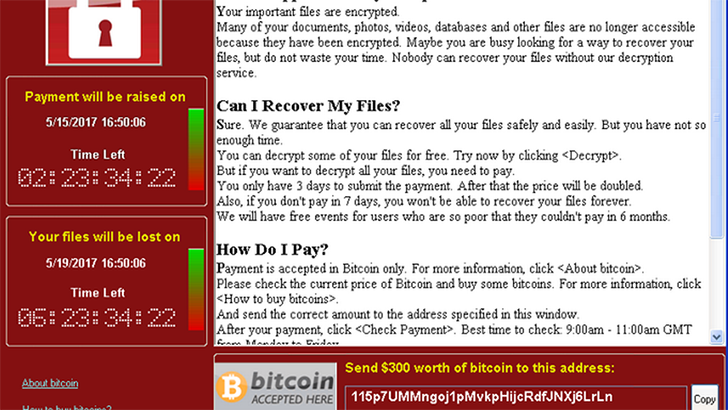
Wanacrypt0r ransom screen

WanaCrypt0r Analysis Part II – SMB Exploit and Worm Component

Introduction Part II of the WanaCrypt0r code analysis has arrived. We’re going to be starting out where we left off last time, which is with the Microsoft Windows MS17-010 Server Message Block (SMB) exploit/”worm component” that made the ransomware so dangerous by allowing it to spread to other vulnerable (not patched) systems on the network

WanaCrypt0r Analysis Part II – SMB Exploit and Worm Component Read More »

Got Apple Quicktime installed on your computer? Uninstall it immediately, says Department of Homeland Security

A recent report from TrendMicro/ZDI stated that Apple has ceased development of Apple Quicktime, and has also revealed two critical vulnerabilities under their Zero Day Initiative. These two vulnerabilities are considered “remote code execution” vulnerabilities, which means a miscreant could get the victim to click on a link or visit a website, and can remotely

Got Apple Quicktime installed on your computer? Uninstall it immediately, says Department of Homeland Security Read More »

Actors behind Dridex launch another spam campaign, delivering Locky Ransomware

Recent reports have indicated that the actors behind Dridex, originally a banking Trojan distributor, have switched tactics, and are now heavily pushing out a new ransomware called Locky. The current method of distribution is via a spam email, which contains a Word document. Additional reports have stated that it is being distributed via the Neutrino

Actors behind Dridex launch another spam campaign, delivering Locky Ransomware Read More »